
For public authorities Security assessment for public bodies
A technical assessment whose documentation is structured from the outset to stand up to an audit and a procurement procedure.
- The key questionWhere is your institution vulnerable – and can this still be documented traceably years later?
- Why it mattersFor public bodies it isn't enough to have tested. It has to be documented, justified and auditable.
- What you have afterwardsReport with CVSS scores, a complete chain of evidence in the portal and documents for the file.
Security assessment for public bodies
- External and internal testing based on OWASP and PTES
- Testing the public area for physical access routes
- Quote with clearly defined service items, suitable as the basis for a direct award
- Non-disclosure agreement before the first meeting
- Complete chain of evidence for each finding: timestamp, evidence, rating, processing status
How it works in practice.
Procurement-ready quote
You receive service items with a transparent calculation. You decide on the applicable procurement route; we supply the documents for it.
Rules of Engagement
Boundaries, time windows, contact persons and escalation paths are set out in writing – on request without subcontractors.
Execution
Technical test plus, if commissioned, an entry attempt via the public area during opening hours.
Documentation
Report and chain of evidence in a form that will still be understandable in three years' time.
A commissioned attack on your own systems. We look for vulnerabilities and exploit them in a controlled way to show how far someone would get. The difference from a real attack: you know about it, it is agreed in writing, and we destroy nothing.
A scan is an automatic list of possible problems – often with many false positives. A pentest checks by hand which of them can actually be exploited. A scan says "this door could be open", a pentest walks through it.
This describes how much we get from you beforehand: nothing, a normal user account or full insight. Which option makes sense depends on your question – we explain it in detail on the basics page.
An internationally standardised scale from 0 to 10 for the severity of a vulnerability. That way "critical" is not our opinion but a traceable rating that your insurer or auditor also knows.
What is included – and what explicitly is not.
Typical scope
One site with an administration network, externally reachable services and a public area.
Duration
Three to eight test days depending on size, report within one week of the end of testing.
Prerequisite
Written commission by the competent body and a named contact person.
Not included
No legal advice on procurement or reporting obligations – we provide the technical side, your legal department makes the classification.
Information on procurement procedures and reporting obligations does not replace legal advice. We prepare our documents according to your requirements.
What people ask beforehand.
Your procurement office decides on the basis of the contract value and the applicable thresholds. We provide a quote with clearly defined items and a transparent calculation that is suitable as a basis for this.
Not by default – DEF.S3C is a sole proprietorship. Should additional capacity be needed for a sub-area, this is named in advance and must be approved by you.
If your institution falls under the Austrian NIS regime, we align the scope and report so that they can be used as evidence of technical risk management measures. Whether the classification applies is something you clarify with your legal department.
Encrypted in a data centre in the EU, automatically deleted no later than 14 days after the end of the mission. On request we hand over a complete archive to you beforehand.
More offers for you.
Security assessment for public bodies
A technical assessment whose documentation is structured from the outset to stand up to an audit and a procurement procedure.
Access test in the public area
Public offices have a feature that hardly occurs elsewhere: strangers in the building are completely normal. That is exactly what we test.
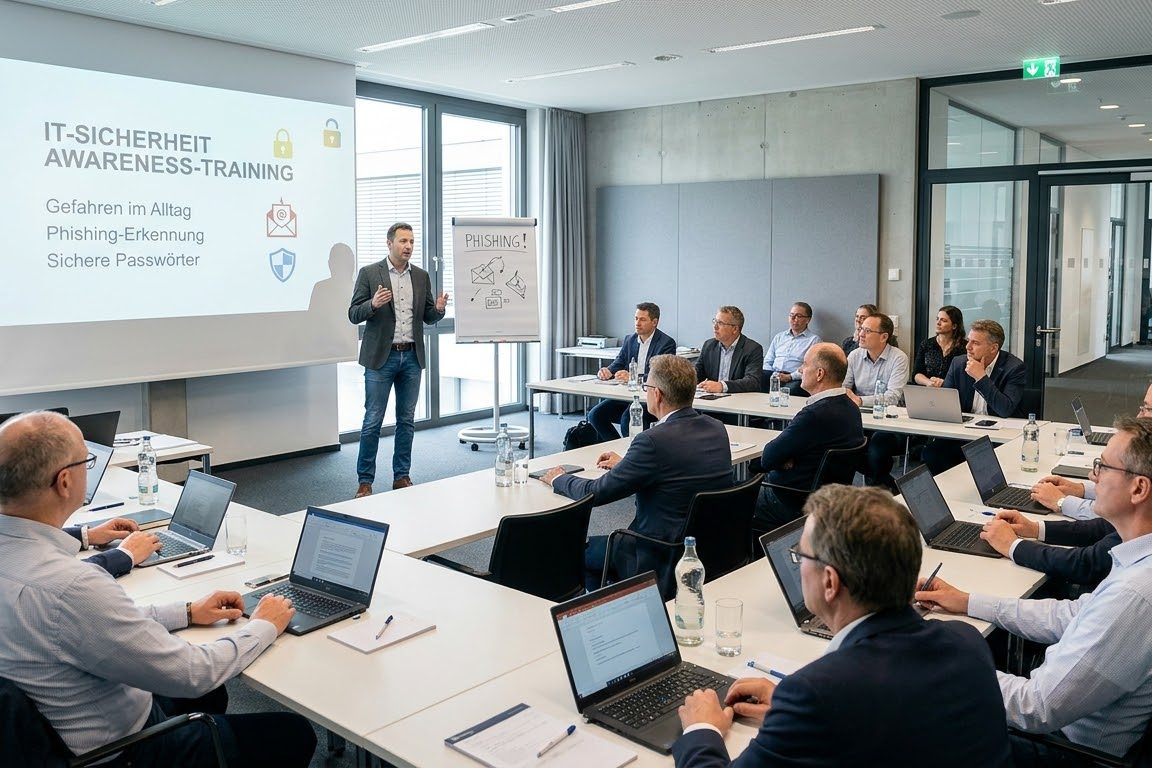
Awareness for public employees
Training and simulation tailored to everyday administrative life: official secrecy, record keeping and a public area where strangers are normal.
What we encounter in assessments, before you encounter it.
Not a product newsletter. We write about attack paths that actually worked against Austrian businesses, authorities and schools – and what helps against them.
- About once a month, not every week
- Concrete attack paths from real assessments
- No tracking pixel, no sharing with advertisers
- Unsubscribe with one click in every email