
Public Authorities Tests that stand up to an audit.
Municipalities, state institutions and public enterprises work under different conditions from a company: procurement law, official secrecy, reporting obligations and documentation that must still be traceable years later. Our approach is designed for this.
What is different in this role.
The same methods, but a different framework: different obligations, different language, different pace.
Procurement-ready quote
You receive a quote with clearly defined service items and a transparent calculation – suitable as the basis for a direct award or as tender documentation. You decide on the applicable procurement route; we supply the documents for it.
Confidentiality
Non-disclosure agreement before the first meeting. On request we work exclusively with named contact persons and without subcontractors.
NIS2 and reporting obligations
If your institution falls under the Austrian NIS regime, we align the scope and report so that it can be used as evidence of your risk management measures. Whether the classification applies is something you clarify with your legal department – we provide the technical side.
Traceable file
Every finding with timestamp, evidence, rating and processing status. The portal provides a closed chain up to the re-test – exactly what a later audit wants to see.
Data sovereignty
All project data is stored encrypted in a data centre in the EU and is deleted no later than 14 days after the end of the mission. On request we hand over a complete archive to you beforehand.
Public contact as attack surface
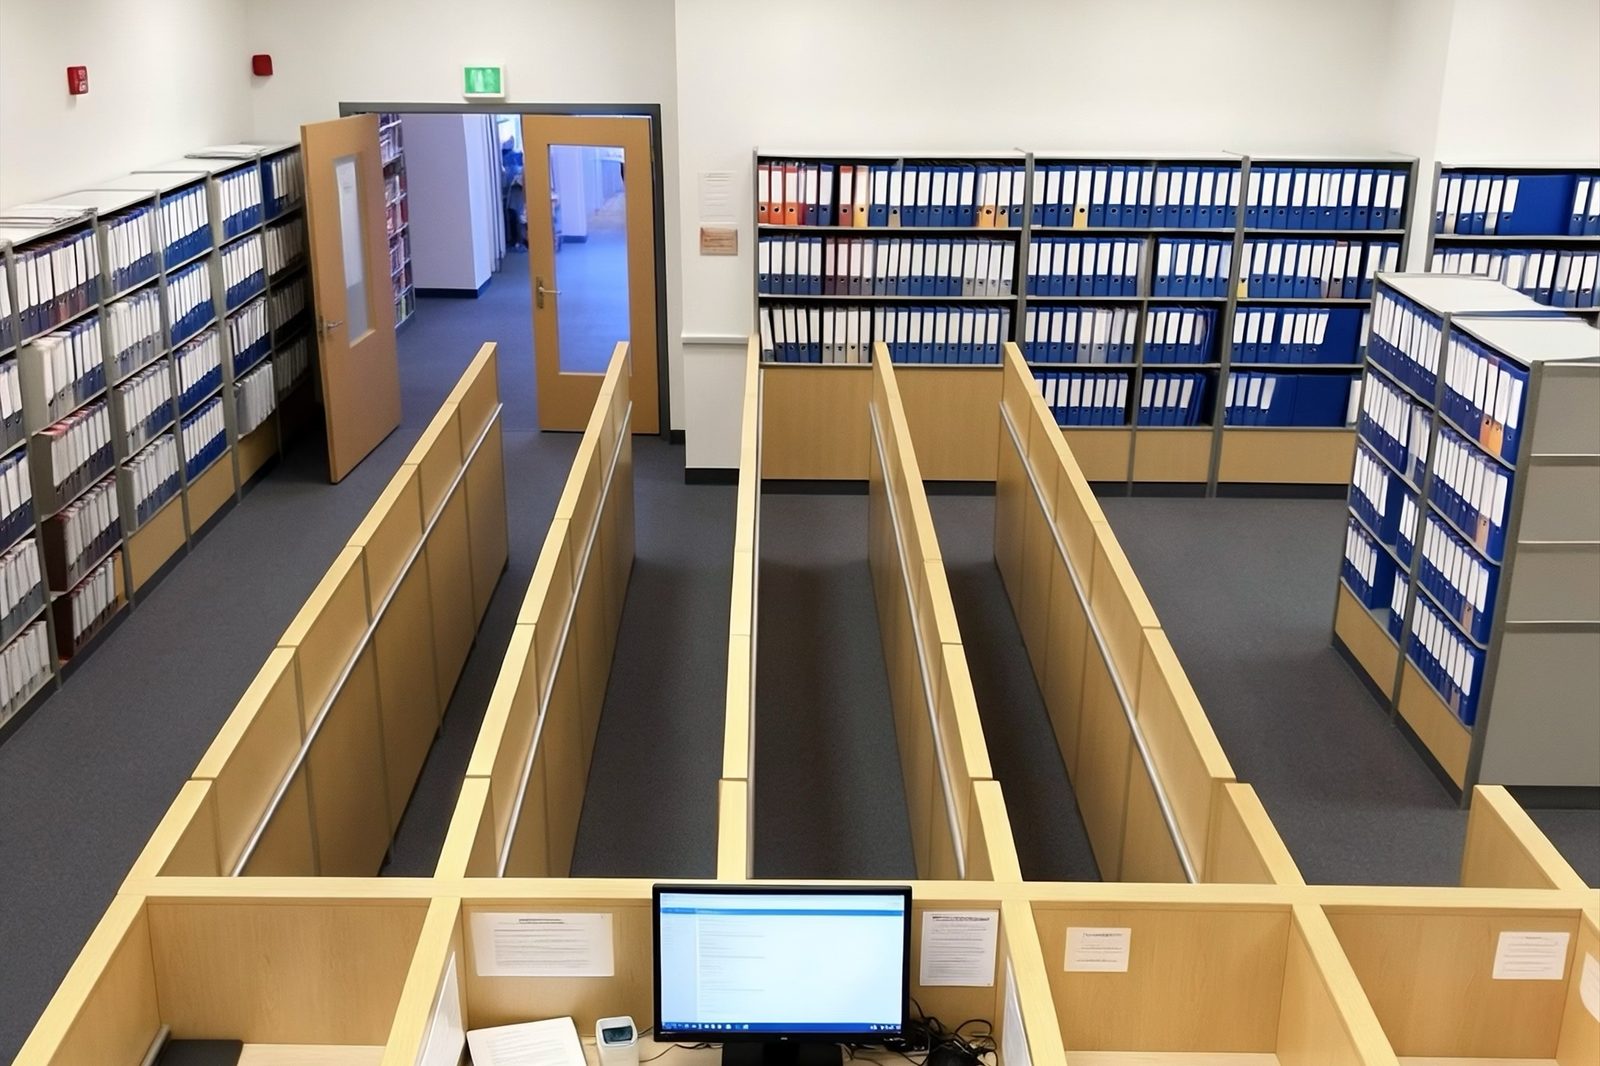
Offices open to the public have one particular feature: strangers in the building are normal. That is exactly what we test – access via the public area, unattended workstations, files at the counter.
Note: information on procurement procedures and reporting obligations does not replace legal advice. We prepare our documents according to your requirements.
The filing cabinet at the counter stays unlocked.
A municipality with public opening hours commissions a test as part of preparing for extended documentation obligations. We test access from the public area to administrative rooms in a simulated out-of-hours scenario, as well as unattended workstations during normal opening hours.
The report clearly distinguishes between findings that can be fixed immediately at no cost – such as a locked screen as a rule – and those that need investment. The municipality uses the report directly as evidence towards the supervisory authority.
Tailored, not copied.
These are dedicated offers for this audience – not the business service with a different heading.
Security assessment for public bodies
A technical assessment whose documentation is structured from the outset to stand up to an audit and a procurement procedure.
Access test in the public area
Public offices have a feature that hardly occurs elsewhere: strangers in the building are completely normal. That is exactly what we test.
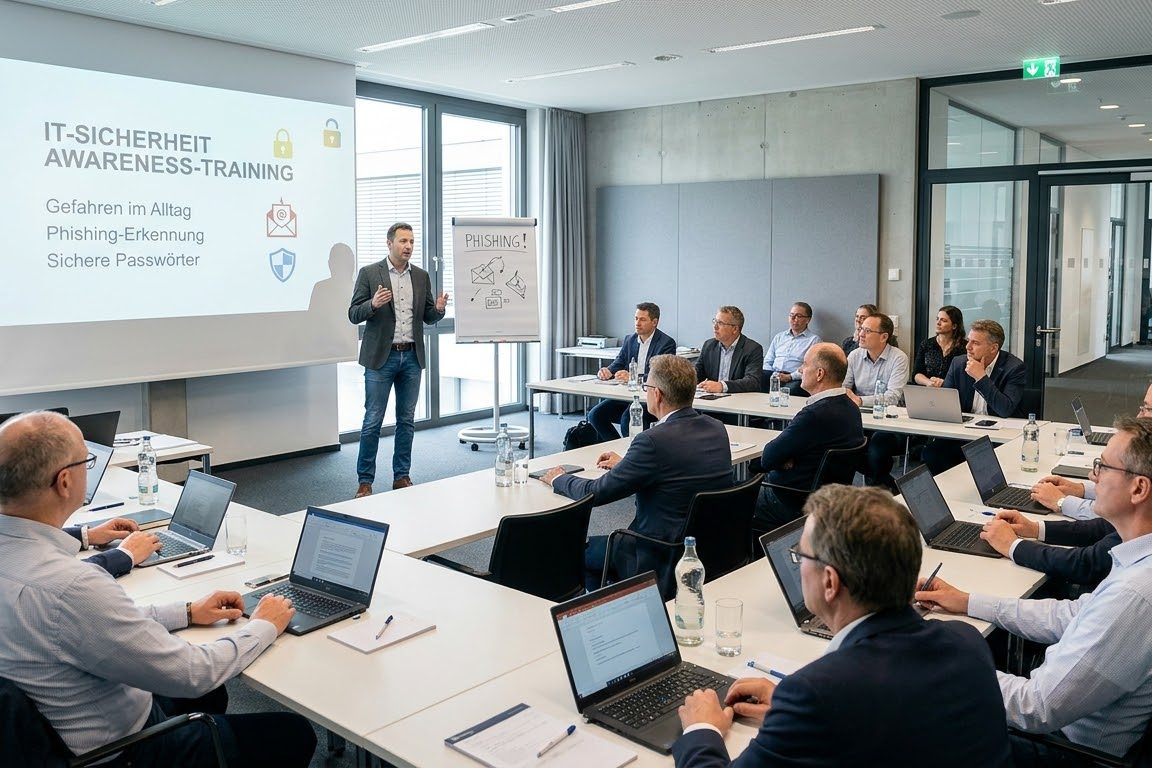
Awareness for public employees
Training and simulation tailored to everyday administrative life: official secrecy, record keeping and a public area where strangers are normal.
What the offers are built on.
The packages above are the most common case. Behind them are our core services — if you need something else, we put it together from them.
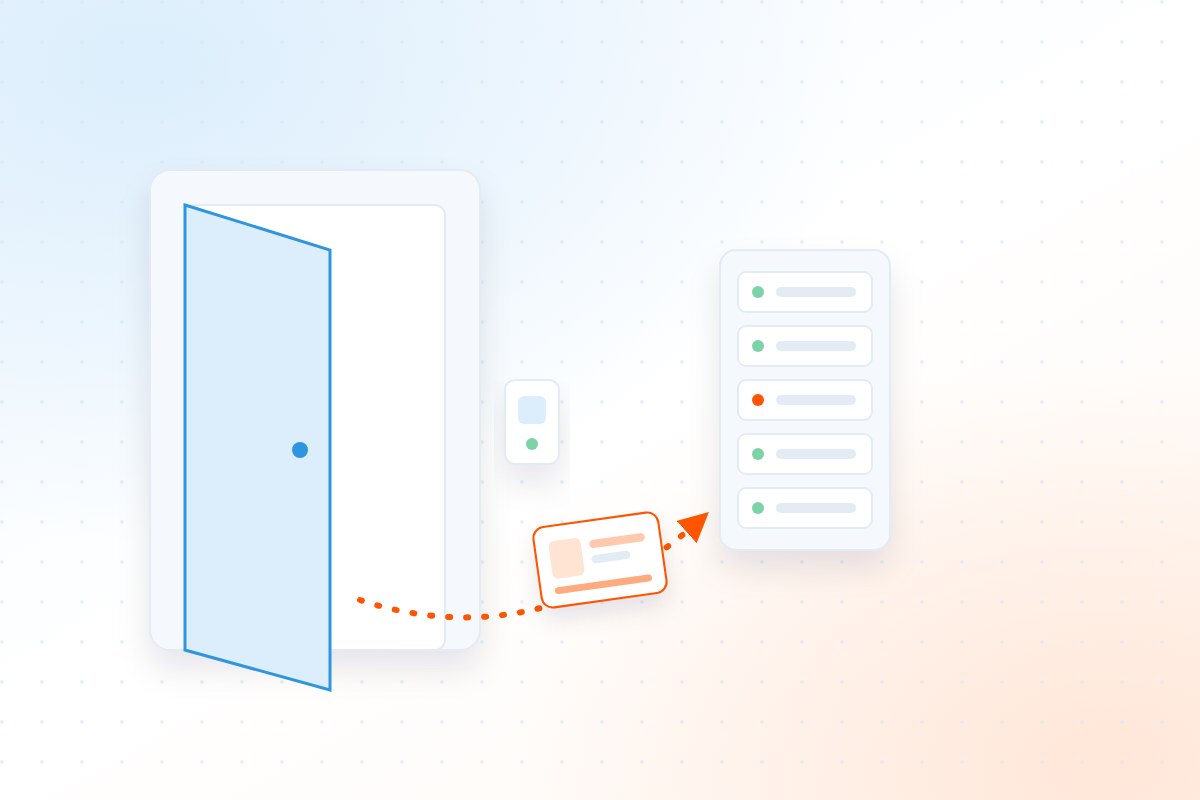
We're standing in your server room.
We get into your building – with the same means as a real attacker, but with your signature in our pocket and a photo as proof.
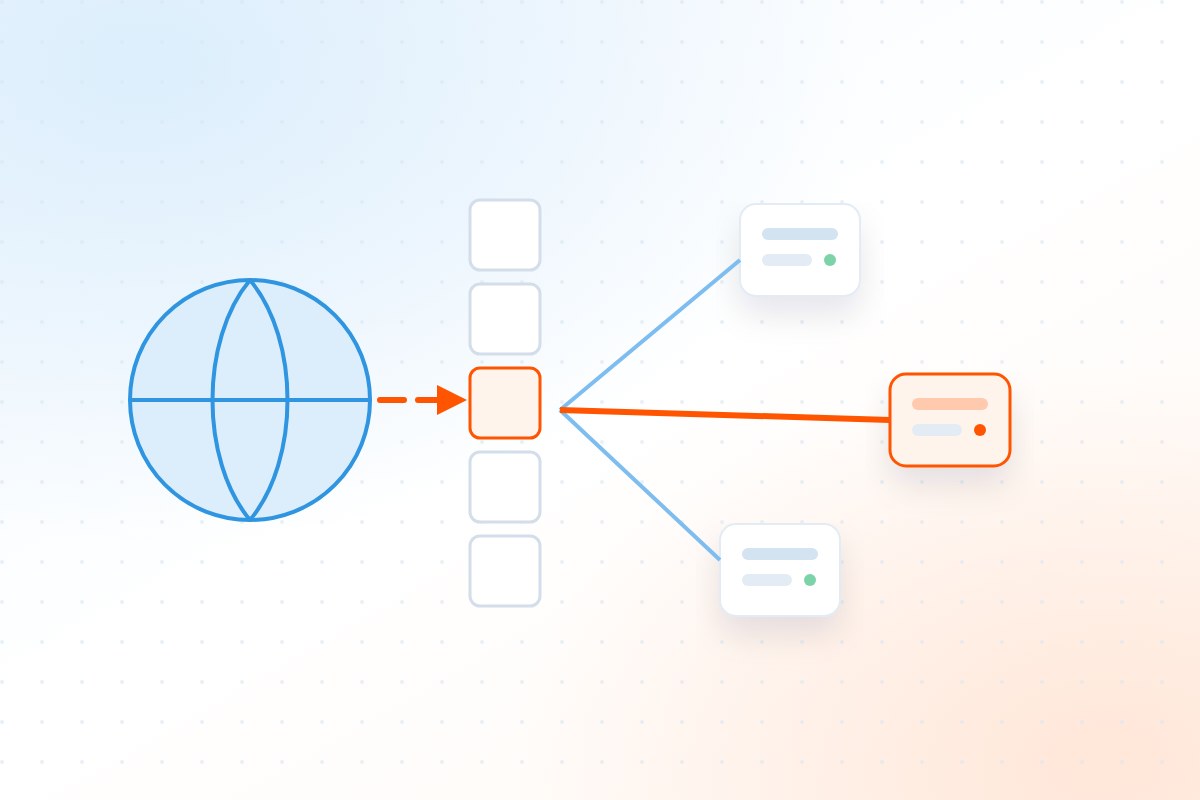
From the outside, like a stranger.
We attack your systems in a controlled way: from the outside like an unknown party, from the inside like an employee whose access has already fallen into the wrong hands.
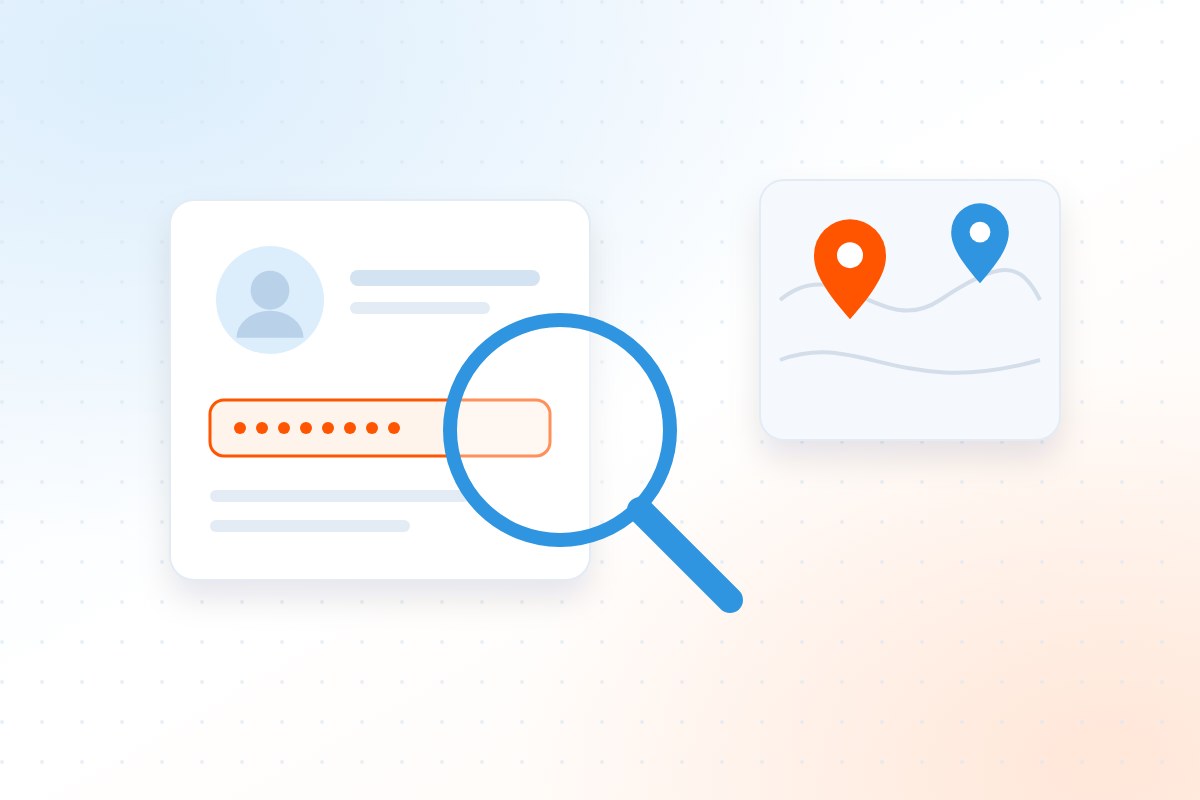
What is already out in the open.
We gather what can be found freely about your organisation before someone else does. Completely passive – we don't touch your systems.
The moment of decision.
Technology can be patched, people can't. We train the decision in the moment of the attack – measurable, repeatable and without singling anyone out.
From the first conversation to the confirmed fix.
Intro call
30 minutes, free of charge. We clarify what you want to protect and where an attacker would start with you. At the end you get an honest assessment of whether a test is the right next step at all.
Scope & rules
Objectives, boundaries, time windows, emergency contacts and escalation paths are put in writing. Without a signed engagement and Rules of Engagement, no test begins with us.
Execution
The test runs and you follow it in the portal. Anything critical we report immediately rather than at the end – so you can react while we are still working.
Report & re-test
You receive all findings with a CVSS score and concrete measures. Once you have implemented them, we test again. Only when that is confirmed is a finding considered closed.
What we encounter in assessments, before you encounter it.
Not a product newsletter. We write about attack paths that actually worked against Austrian businesses, authorities and schools – and what helps against them.
- About once a month, not every week
- Concrete attack paths from real assessments
- No tracking pixel, no sharing with advertisers
- Unsubscribe with one click in every email