
For businesses with walk-in customers Access, POS and Customer Data Check
For studios with access outside staffed hours, practices, workshops and restaurants: we look at where people actually get to — and what is there.
- The key questionDoes someone with a normal access card get further than you think?
- The classicAll card readers were put into the same group during installation — the training card also opens the office.
- What you have afterwardsClearly separated areas and a workstation where the member database isn't left open.
Access, POS and Customer Data Check
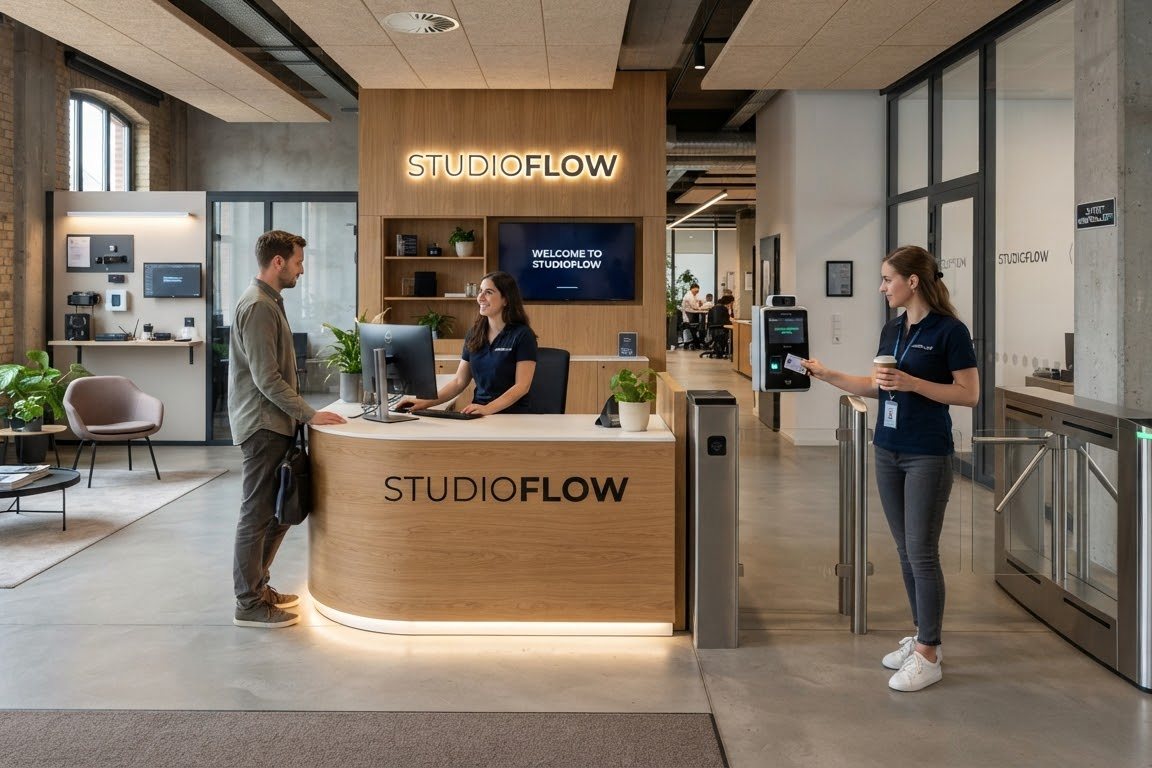
- Review of access rights: which card opens which door, and why
- Hours outside staffed times — precisely when nobody is there to challenge anyone
- Back-office workstations: screen lock, till system, member database
- Key cabinets, side entrances, delivery access and emergency exits from outside
- Cameras: where they point, who sees the footage and whether the signage is correct
How it works in practice.
Agree
We set out in writing what is tested and what remains off limits.
Walk through
One walkthrough during normal hours, one outside staffed hours.
Document
Every finding with photo and timestamp, in the portal the same day.
Discuss
What costs nothing and can be done today, what needs investment?
We try to get into your building – the way someone with bad intentions would. Not secretly behind your back, but commissioned and agreed in writing. At the end you know how far someone gets and where something stops them.
Simply walking in behind someone who holds the door open. No trick, no technology – just politeness working against you. The most common way into a building.
Many access cards transmit their ID unencrypted. A reader in a bag is enough to read it in passing and write it onto a blank card. The person affected notices nothing.
An inconspicuous device that we plug into a network socket. It establishes a connection to the outside. This answers a question that otherwise remains theory: does your IT even notice a foreign device on the network?
What is included – and what explicitly is not.
Typical scope
One site with public and staff areas, access system and till.
Duration
One to two days, depending on size and opening hours.
Prerequisite
Written commission and signed Rules of Engagement. Without these two documents we don't enter anything.
Not included
No installation of locks or access technology, no legal advice on video surveillance.
We test and document. Your installer takes care of fitting locks, readers or cameras — we tell you what they need to be able to do.
What people ask beforehand.
You decide. Both options have their value: announced, you test the technology; unannounced, you also test the reaction. For unannounced tests we agree beforehand who is informed so that nobody calls the police.
Then it is less about access technology than about what is inside: the unlocked till, the customer file, the labelled key cabinet. The appointment is correspondingly shorter.
Then we document it and report it to you immediately — we take nothing and change nothing. That is exactly what the engagement is for: so that you hear it from us and not from someone else.
More offers for you.
Security baseline check
The starting point for businesses that have never been tested: we look at your organisation from the outside and tell you in plain language where you stand.
Red team engagement
Building and network in one engagement: we try to get in – physically and digitally – and document every step.
Phishing simulation & training
A realistic simulation, followed by a short training session based on the real cases from your organisation – and a second measurement that shows whether it worked.
Access, POS and Customer Data Check
For studios with access outside staffed hours, practices, workshops and restaurants: we look at where people actually get to — and what is there.
What we encounter in assessments, before you encounter it.
Not a product newsletter. We write about attack paths that actually worked against Austrian businesses, authorities and schools – and what helps against them.
- About once a month, not every week
- Concrete attack paths from real assessments
- No tracking pixel, no sharing with advertisers
- Unsubscribe with one click in every email