
For companies Red team engagement
Building and network in one engagement: we try to get in – physically and digitally – and document every step.
- Who we serveBusinesses with valuable assets on site: production, laboratory, server room, archive.
- The key questionNot whether someone gets in, but how far they get before someone asks.
- What you have afterwardsFindings with photo evidence and an answer to the question of which control really works in everyday life.
Red team engagement
- Reconnaissance from publicly available sources beforehand
- Entry attempts via several routes and at different times of day
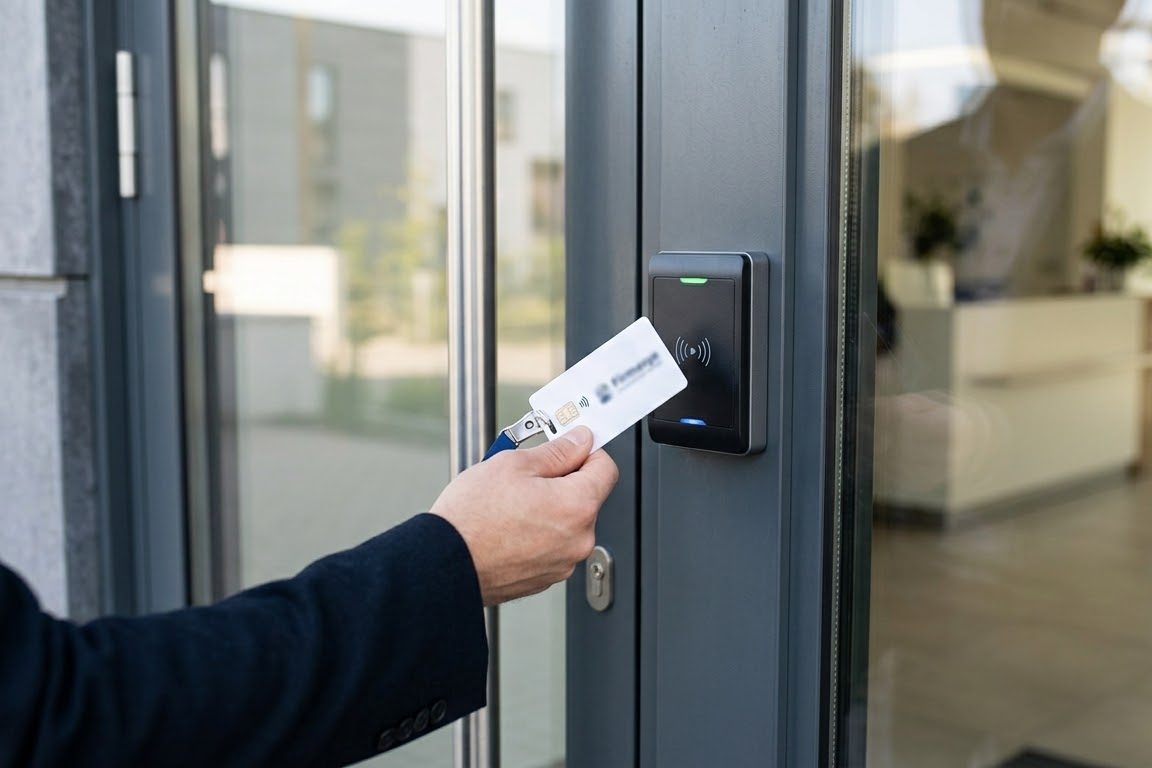
- Testing access cards for copyability
- Rogue device on the network: does your monitoring notice a foreign device?
- Subsequent internal test from the access gained
How it works in practice.
Reconnaissance
Building layout, shift changes, suppliers, badge design – all from publicly accessible sources.
Access
Several routes in parallel: main entrance, delivery area, underground car park. Every attempt is logged, including the failed ones.
Depth
What can be reached from the first room – network socket, server room, unattended workstation?
Wrap-up
Joint review meeting with a photo series. In our experience the most effective part of the entire project.
We try to get into your building – the way someone with bad intentions would. Not secretly behind your back, but commissioned and agreed in writing. At the end you know how far someone gets and where something stops them.
Simply walking in behind someone who holds the door open. No trick, no technology – just politeness working against you. The most common way into a building.
Many access cards transmit their ID unencrypted. A reader in a bag is enough to read it in passing and write it onto a blank card. The person affected notices nothing.
An inconspicuous device that we plug into a network socket. It establishes a connection to the outside. This answers a question that otherwise remains theory: does your IT even notice a foreign device on the network?
What is included – and what explicitly is not.
Typical scope
One site, one to three entry attempts, subsequent internal test.
Duration
Three to five days, spread over several dates.
Prerequisite
Written commission, signed Rules of Engagement and an escalation contact who can be reached at any time.
Not included
No burglary in the criminal sense: we damage nothing and do not enter excluded areas.
A red team engagement is a sample, not proof of completeness. It shows that a way in exists – not that it is the only one.
What people ask beforehand.
Only a small circle named by you. The test examines real everyday life, and that can't be tested if everyone is prepared. The evaluation is exclusively anonymous – nobody is named.
Then the test has ended successfully at that point and we document what worked. Attempts that were stopped are valuable results, not failures.
It depends on what you have on site. Anyone with customer data, design documents or a production control system in the building is a worthwhile target – regardless of the number of employees.
More offers for you.
Security baseline check
The starting point for businesses that have never been tested: we look at your organisation from the outside and tell you in plain language where you stand.
Red team engagement
Building and network in one engagement: we try to get in – physically and digitally – and document every step.
Phishing simulation & training
A realistic simulation, followed by a short training session based on the real cases from your organisation – and a second measurement that shows whether it worked.
Access, POS and Customer Data Check
For studios with access outside staffed hours, practices, workshops and restaurants: we look at where people actually get to — and what is there.
What we encounter in assessments, before you encounter it.
Not a product newsletter. We write about attack paths that actually worked against Austrian businesses, authorities and schools – and what helps against them.
- About once a month, not every week
- Concrete attack paths from real assessments
- No tracking pixel, no sharing with advertisers
- Unsubscribe with one click in every email